Does Change Enforcement stop every change?+
It stops changes outside the protected server's known-good baseline, with protections turned on, at the point of execution. Changes inside the baseline run. In Active Mode, the node observes and reports. It enforces once a configuration with protections turned on is applied. In Maintenance Mode, Mimic suspends enforcement and keeps monitoring. Every change, authorized and unauthorized, goes on the record.
Is change enforcement the same thing as change control?+
They work together. Change control is the discipline: your process decides whether a change should happen and keeps the request and the approval. Change enforcement acts on the server itself, at the point of execution. Mimic Networks Change Enforcement holds a protected server to its known-good baseline and, with protections turned on, stops a change outside it.
Does it replace our file integrity monitoring?+
It runs beside it. Mimic runs alongside FIM tools. File integrity monitoring reports a change after it lands, and some standards name it directly. Change Enforcement acts at the point of execution and records every change on the servers Mimic protects. Where a standard requires file integrity monitoring, keep your FIM tool and check the requirement with your assessor.
Do Change Enforcement and Ransomware Defense depend on each other?+
No, they're separate products. With protections turned on, Change Enforcement stops a change outside the protected server's known-good baseline at the point of execution on its own, without Ransomware Defense, and every change, authorized and unauthorized, goes on the record for security and GRC teams. Ransomware Defense doesn't need Change Enforcement either.
Can it open tickets in ServiceNow?+
Through a custom deployment. Mimic integrates with ServiceNow through custom deployments for automated ticketing and change management. Each one is built for your instance rather than installed as a packaged connector, so plan it with your ServiceNow owners before you build workflows around it. Start with the change approvals your auditors already check.
Which events reach our SIEM and SOAR platforms?+
Mimic feeds enforcement events to your security information and event management (SIEM) and security orchestration, automation and response (SOAR) platforms, so your security operations team sees them alongside the rest of its telemetry. You choose which events Mimic passes to them, so your detections and playbooks get the ones they need.
Does the record cover changes made with valid admin credentials?+
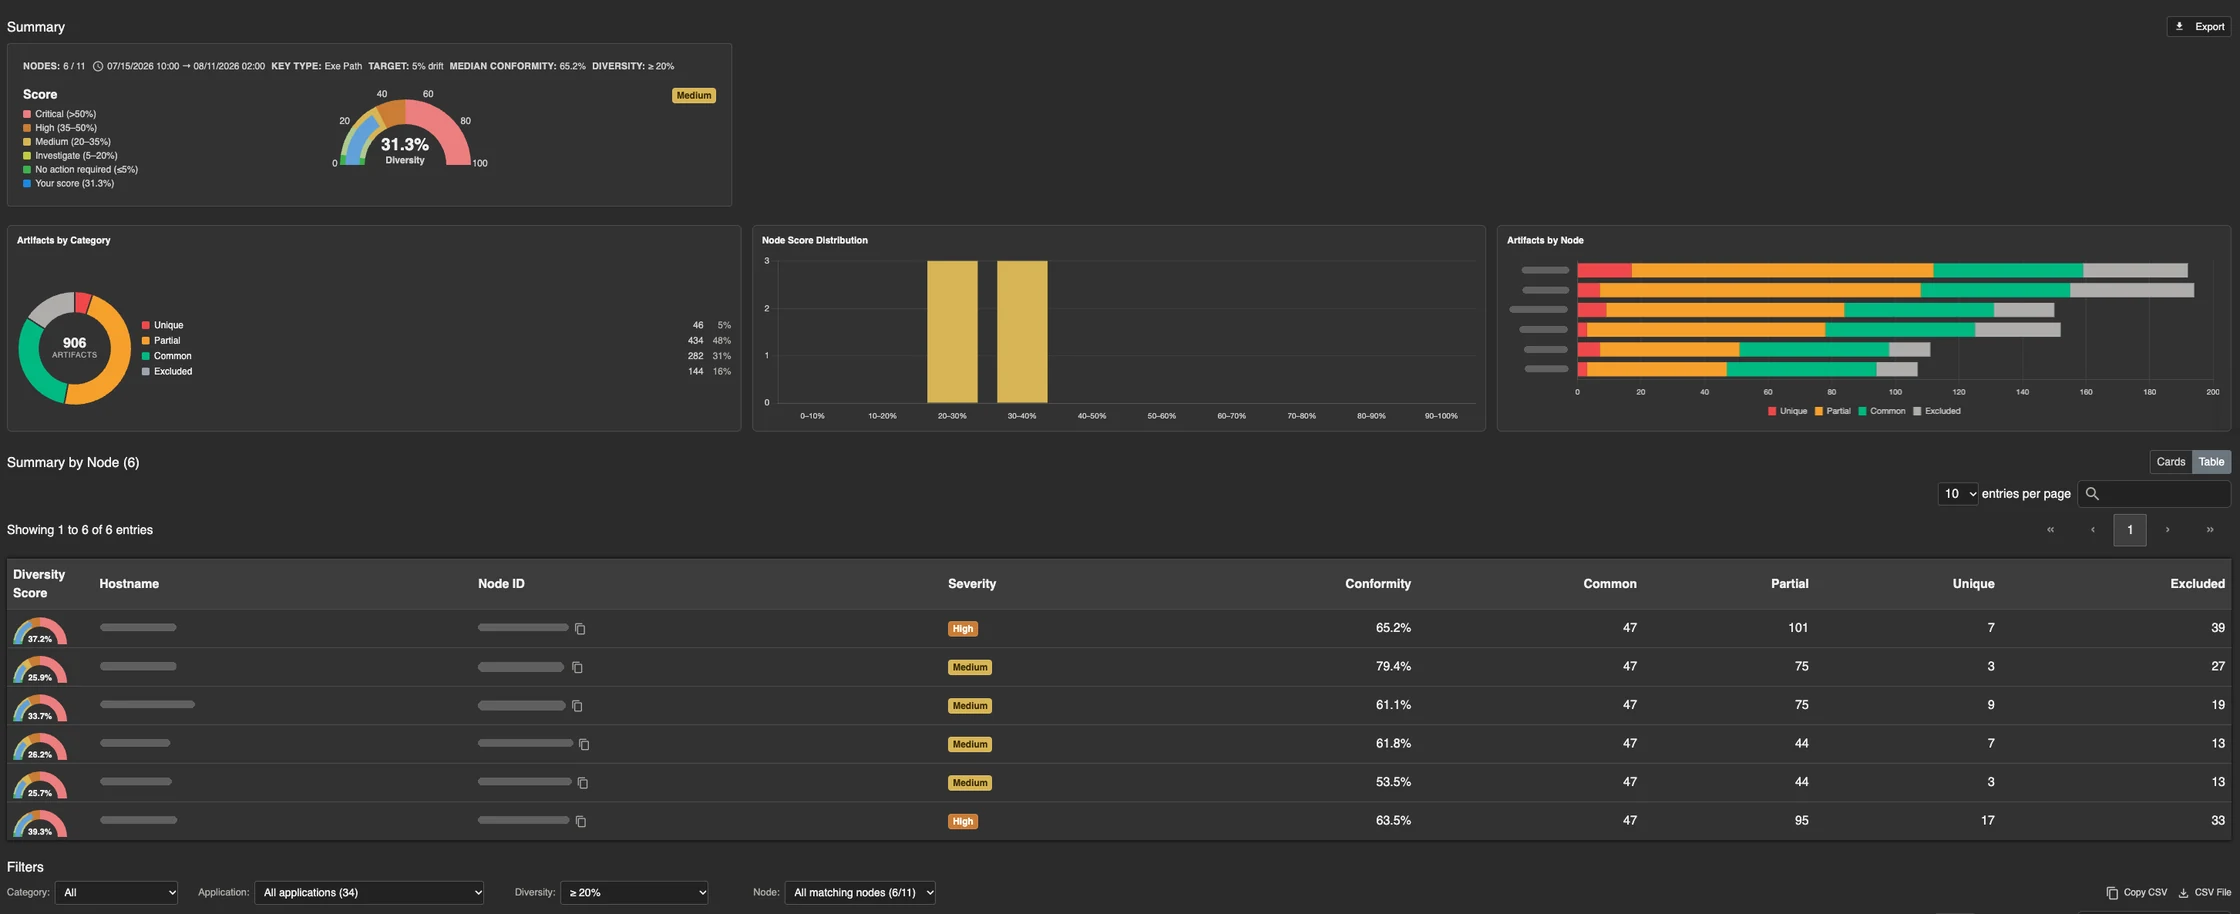
Yes. Change Enforcement monitors and tracks every change on a protected server, authorized and unauthorized, whichever account makes it. A valid administrator credential doesn't take a change out of the record, so your team can review changes made through trusted accounts in DashCam and the Management Plane beside every other change.
How long does Mimic keep the record?+
At least two months. Mimic records every change it monitors at the kernel level, such as file reads and writes, processes and the registry. Your team reviews the record in DashCam and the Management Plane, Mimic's dashboard. To keep events longer, pass the ones you need to your SIEM and SOAR platforms, where your own retention policy applies.
What does it need on each server?+
A Mimic node on a supported server. Mimic protects Windows Server 2016 and later, and Red Hat Enterprise Linux 8 and later. It doesn't run on laptops, desktops or network devices. No reboots required. Start with the servers your auditors and incident responders ask about most, and widen coverage from there.
Does Change Enforcement add overhead on the server?+
Enforcement overhead is tunable. You set it to an allowable amount through policy on the node, so the people who own each server decide what it can spare. Agree on that amount before the proof of concept, then measure it there on your own servers before you widen coverage across the fleet.
What should we plan for in a maintenance window?+
In Maintenance Mode, Mimic suspends enforcement and keeps monitoring. Recording continues, so the window is a gap in enforcement, not in the record. Plan it like any other change: put a server in Maintenance Mode only for the work you approved, only for as long as the work takes and with the same approvals you'd want for the change itself. Review what changed before you close the window.
Will an auditor accept the record as evidence?+
Your auditor decides what counts as evidence. What Change Enforcement gives them is a record from the protected server itself: every change, authorized and unauthorized. That record supports controls such as DORA Article 9(4)(e) and NERC CIP-010-4 Part 1.2, and it sits beside your tickets and approvals, so an auditor can compare what your change board approved with what changed.